Encrypted in the browser
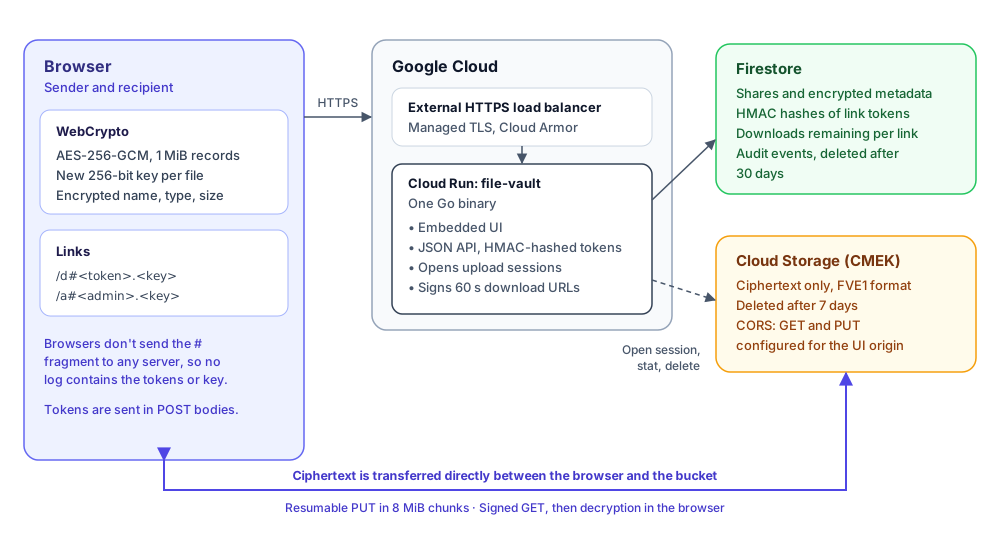
Files and their names are encrypted with AES-256-GCM before upload. The server and the bucket only store ciphertext. The key is in the URL fragment, which browsers don’t send to servers.
Encrypted in the browser
Files and their names are encrypted with AES-256-GCM before upload. The server and the bucket only store ciphertext. The key is in the URL fragment, which browsers don’t send to servers.
Expiring, limited-use links
Each download link has its own expiry (1 hour to 7 days) and use count (1 to 100). Shares are deleted after 7 days.
Link previews don't count
Opening a link only checks it. A download is counted when the recipient clicks Download, so Slack, Outlook or iMessage previews don’t use up a one-time link.
No accounts
Links are the credentials. Tokens are random 256-bit values, stored as HMAC hashes, and never appear in a URL path, so request logs can’t leak them.
One small service
A single Go binary serves the UI and the API on Cloud Run. Uploads and downloads go directly between the browser and Cloud Storage.
Deployed by GitHub Actions
Terraform for the infrastructure, Workload Identity Federation for CI, no keys. Nothing deployment-specific lives in the repository.
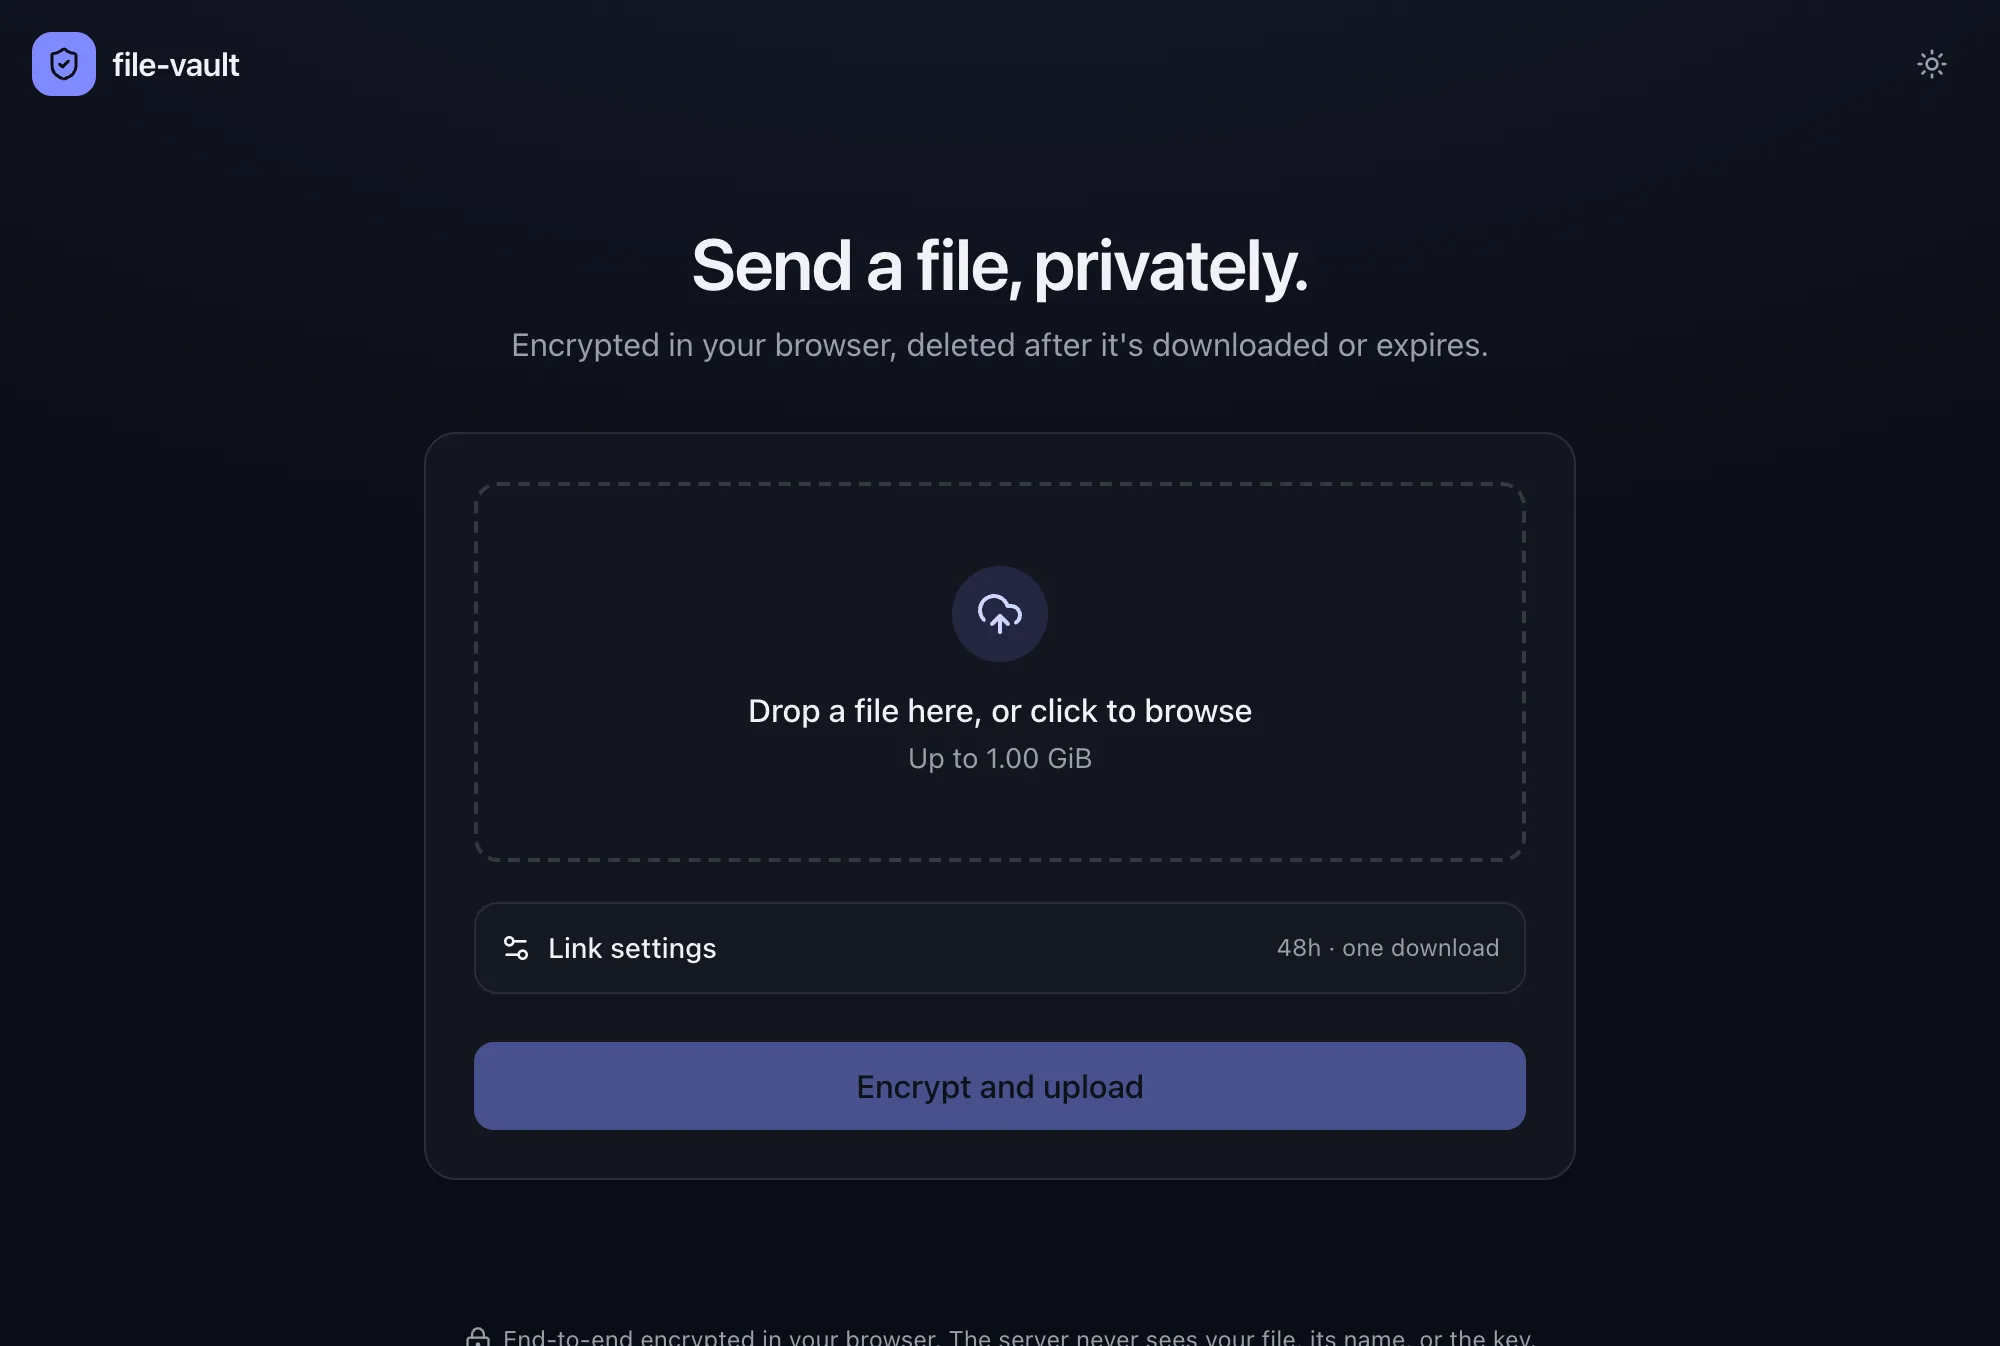
Pick a file and the link settings. The browser encrypts the file before anything leaves it.
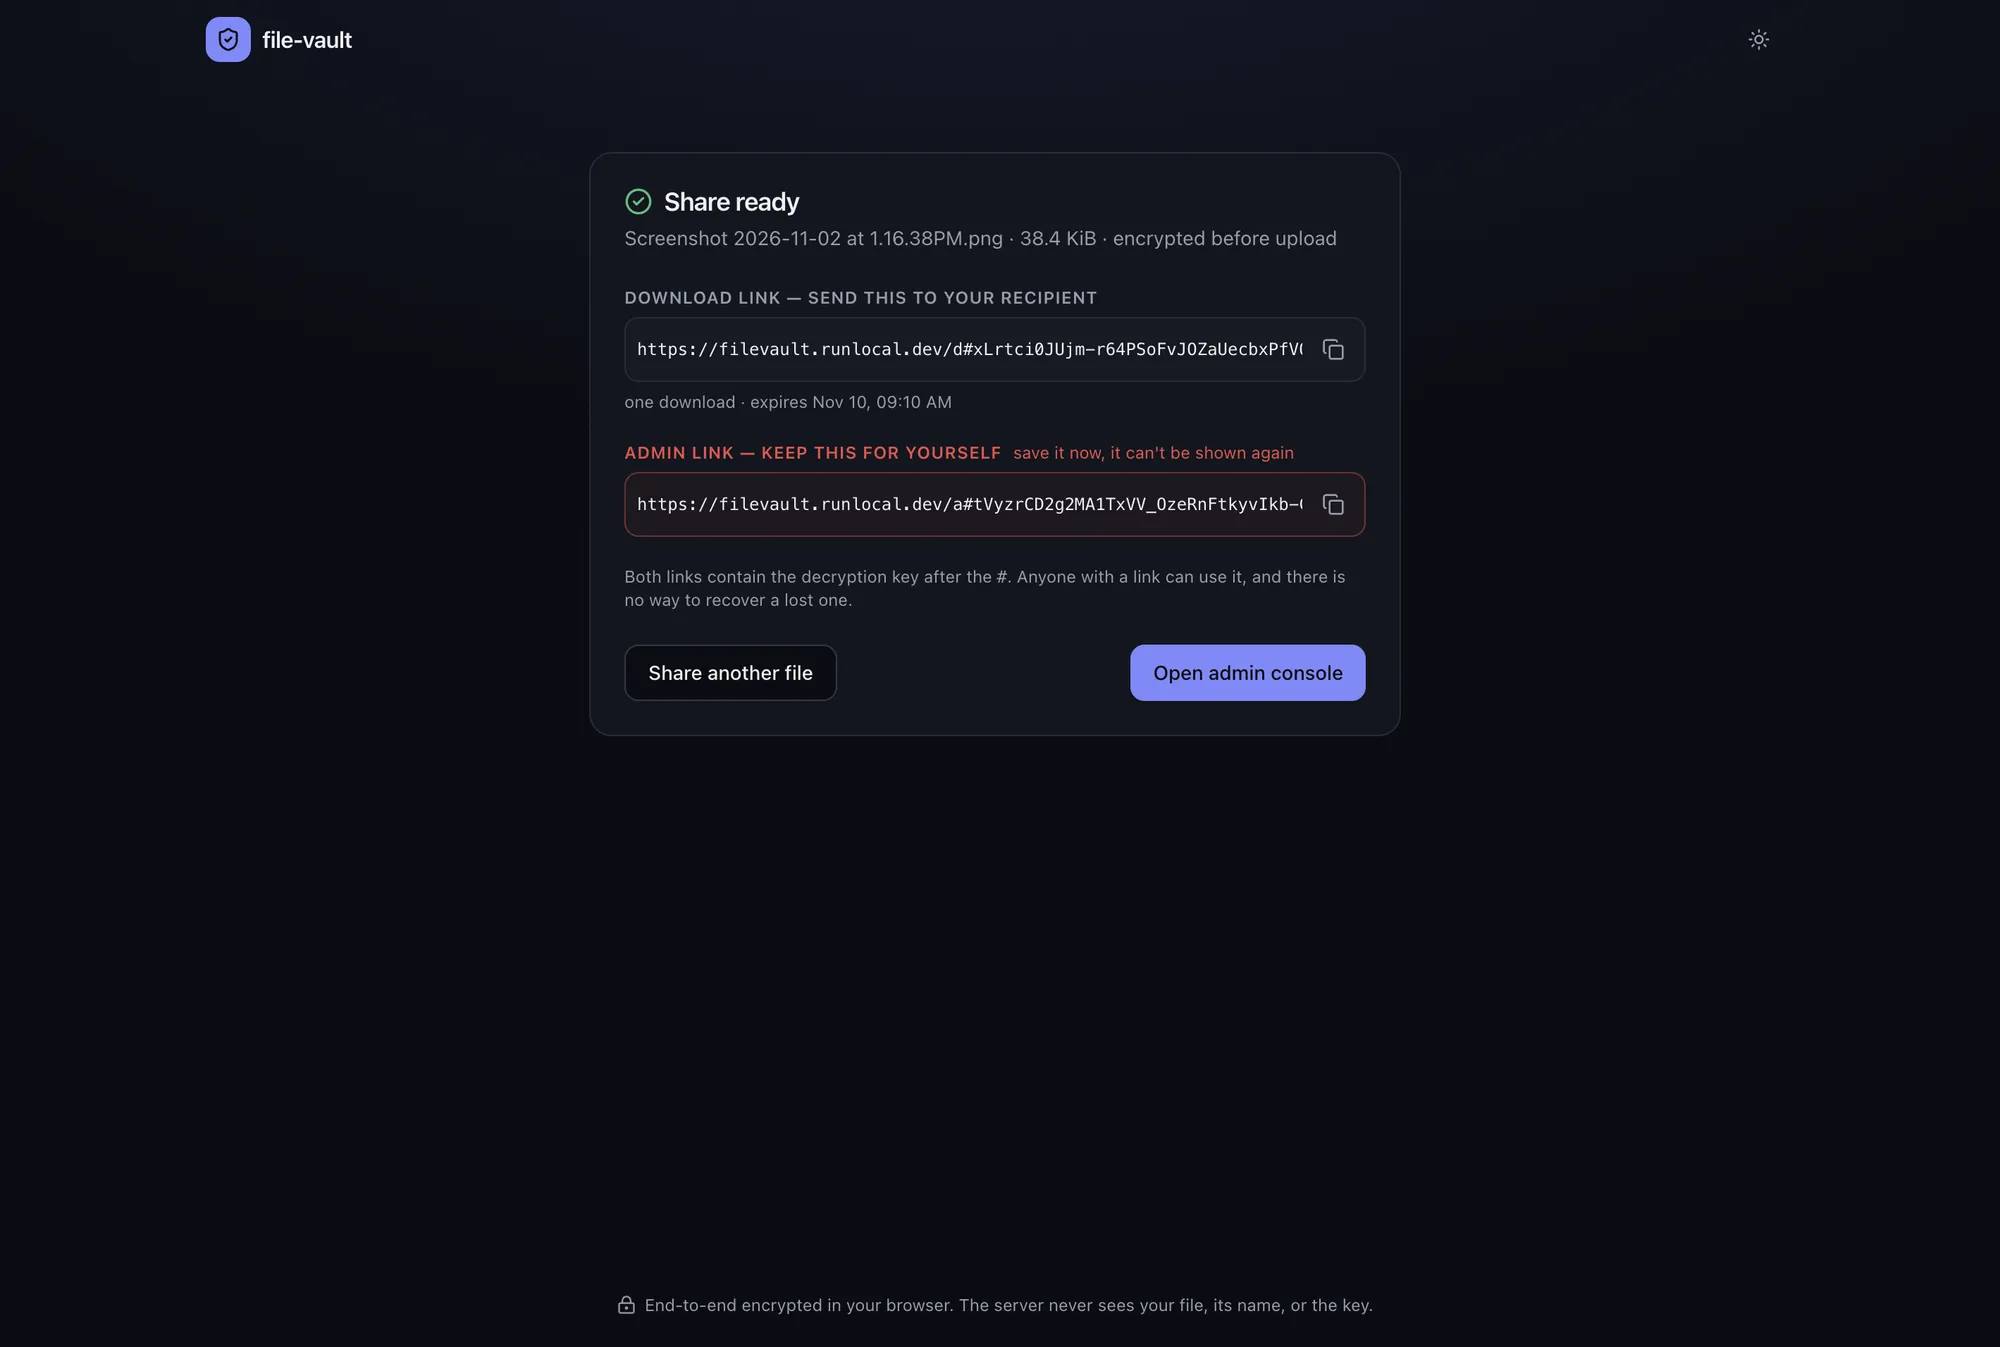
You get two links: one for your recipient, one to manage the share. Both carry the key after the #.
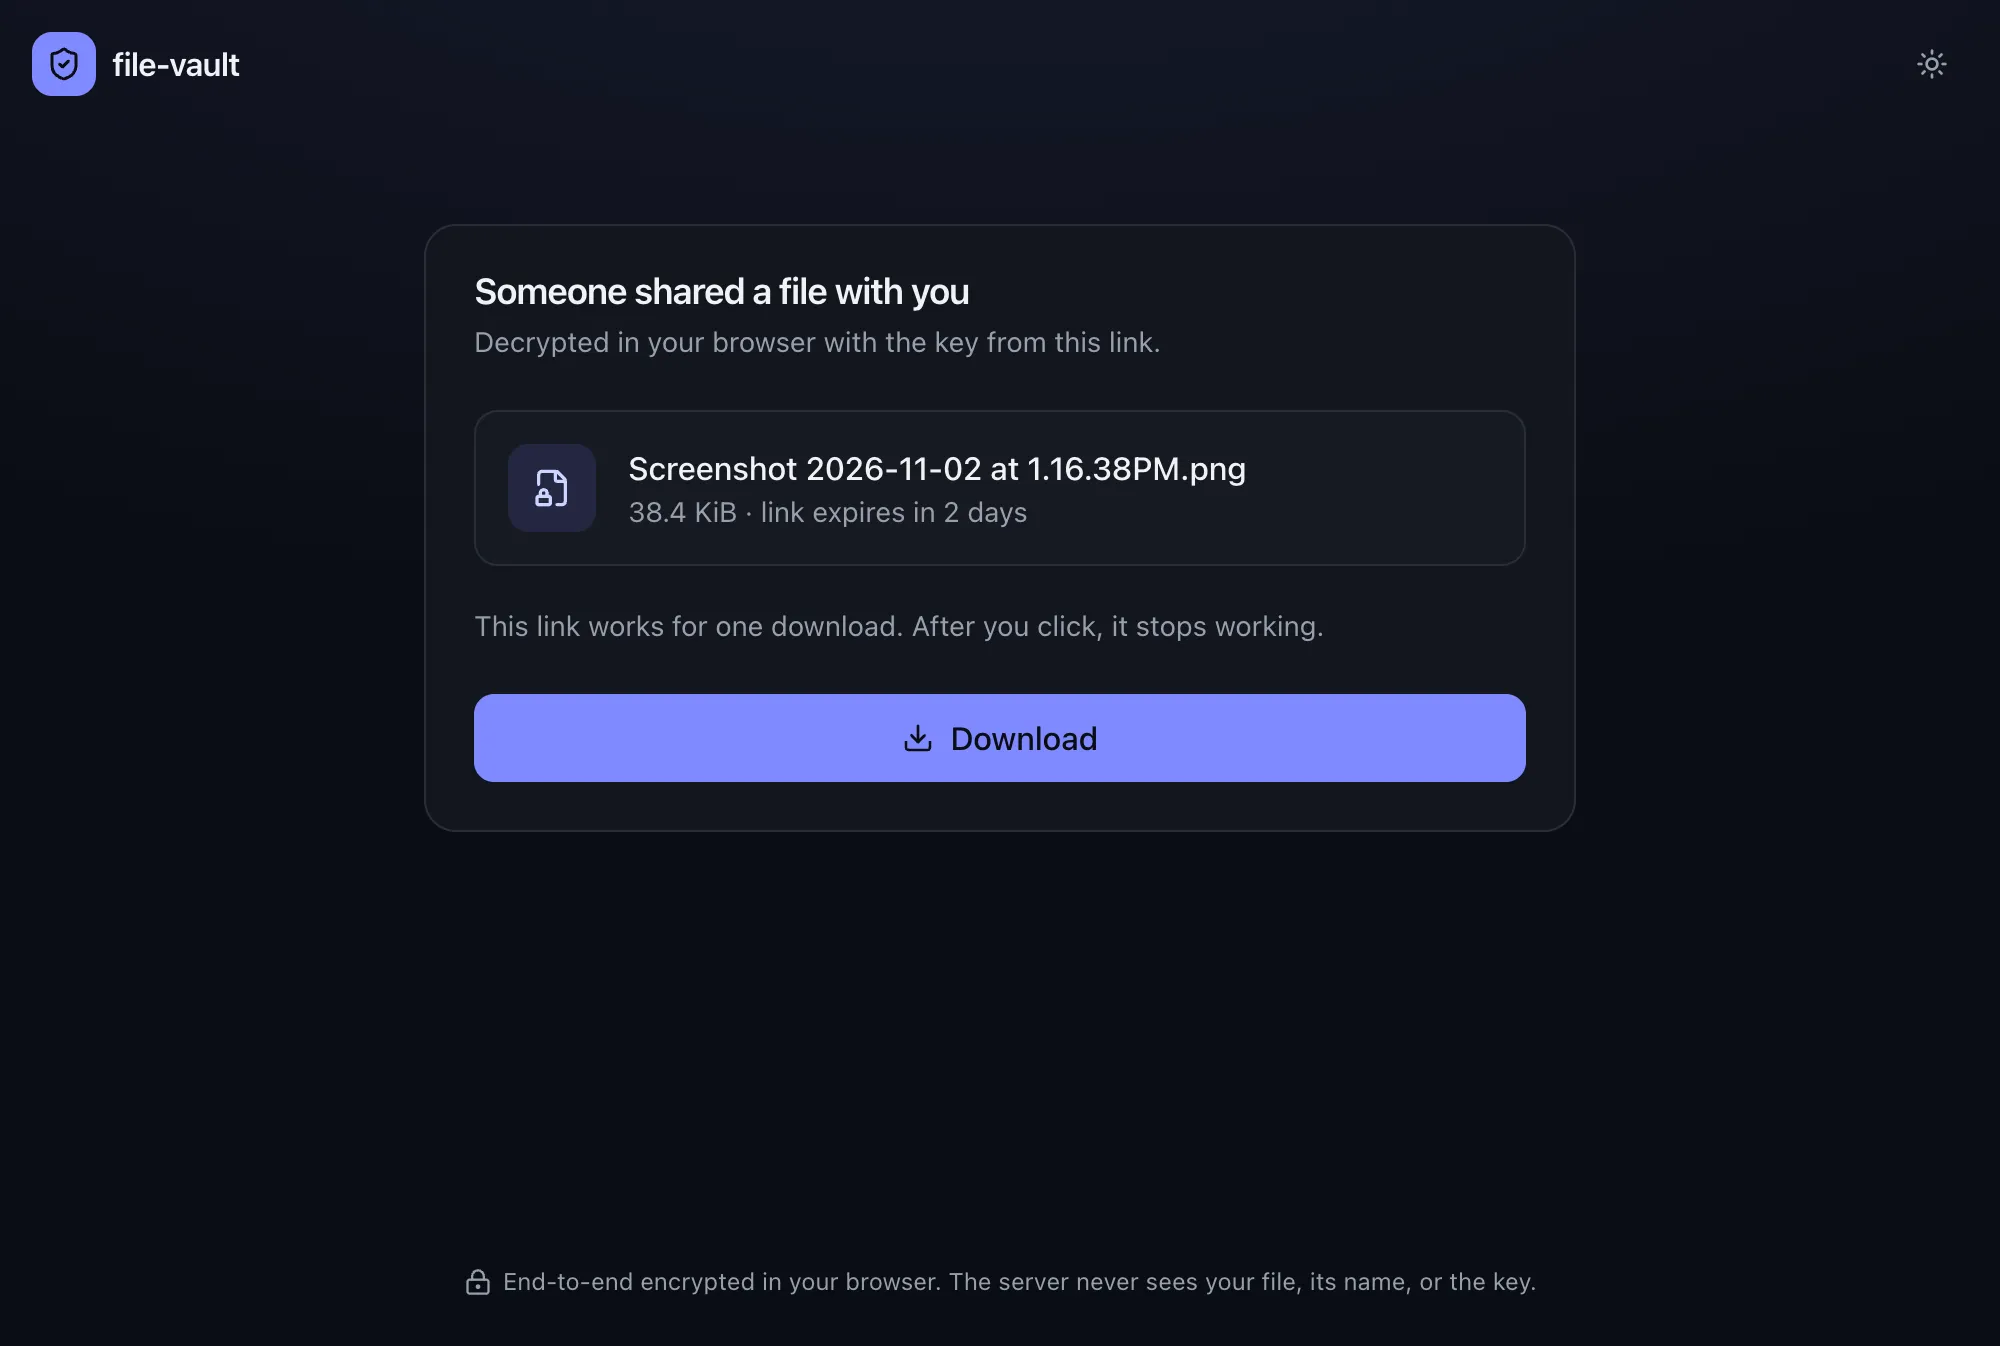
The recipient sees the decrypted file name. Opening the page doesn’t count as a download; clicking Download does.
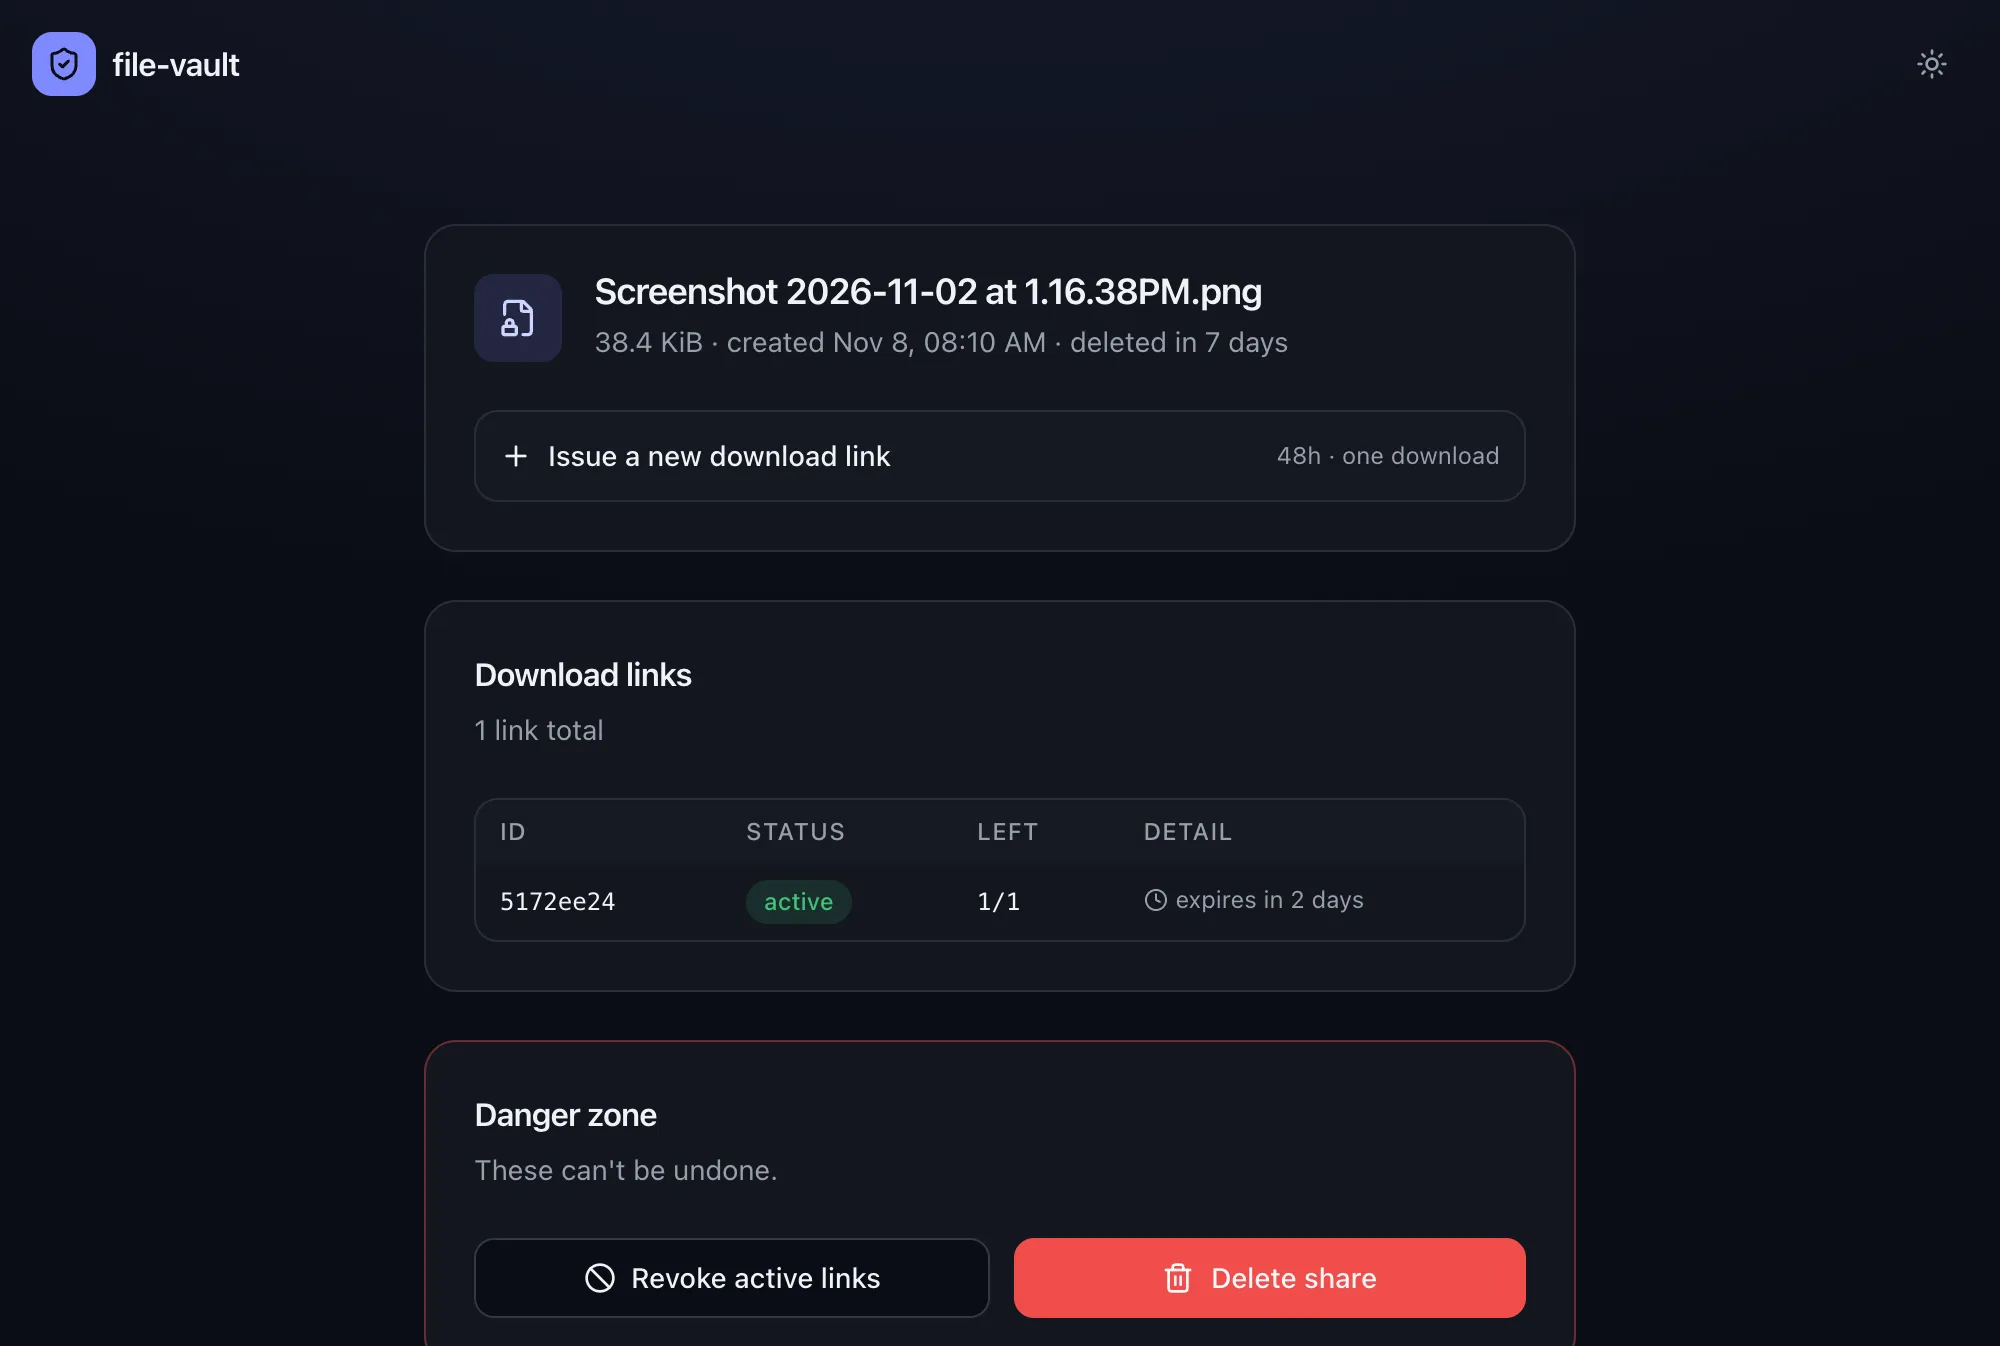
Track each link’s uses, issue new links, revoke them, or delete the share.